Grafana Source Code Stolen Via Compromised GitHub Token
Grafana Labs confirms source code stolen after attackers compromised GitHub environment with stolen access token. Another reminder that token security is critical.
Grafana Labs confirms source code stolen after attackers compromised GitHub environment with stolen access token. Another reminder that token security is critical.
The wp2shell exploit framework is actively targeting WordPress installations through malicious file upload vulnerabilities, enabling attackers to establish persistent web shells on compromised servers. Visitors to infected sites face risks including malware distribution, credential theft, and browse
Two critical vulnerabilities in WordPress Core (CVE-2026-60137 and CVE-2026-63030) are being actively exploited in the wild through a campaign dubbed “WP2Shell.” These flaws allow unauthenticated attackers to achieve remote code execution and complete site takeover on millions of WordPress installat
International law enforcement has successfully dismantled AudiA6, a sophisticated cryptocurrency laundering service that processed over $380 million in ransomware proceeds. The operation resulted in arrests, server seizures, and disruption of a critical financial infrastructure that supported multip
The U.S. State Department has announced a combined $10 million reward for information leading to the identification or location of members from two Russian hacking groups—UNC5792 and UNC4221—who have been actively targeting users of encrypted messaging platforms including WhatsApp and Signal. These
Microsoft brings back resizable taskbar and Start menu to Windows 11. A small UI change that could have big security implications for enterprise environments.
CISA has added CVE-2026-45247, a critical remote code execution (RCE) vulnerability in Adobe Magento, to its Known Exploited Vulnerabilities (KEV) catalog. The flaw is being actively exploited in the wild, allowing attackers to execute arbitrary code on vulnerable e-commerce platforms. Federal agenc
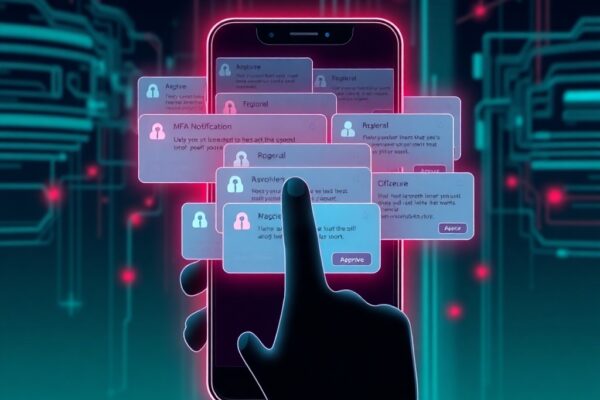
MFA prompt bombing, also known as MFA fatigue attacks, exploits human psychology rather than technical vulnerabilities. Attackers who have already stolen credentials flood victims with dozens or hundreds of push notification authentication requests until users accidentally approve one or simply acce
Threat actors are increasingly abusing legitimate system administration and software deployment tools to deliver malware while evading detection. By leveraging trusted binaries like PowerShell, Windows Management Instrumentation (WMI), and legitimate remote access software, attackers bypass traditio
Cyber Breaches Meet Wall Street Trading Strategies